What ISACA GRC 2026 Made Clear About the Future of Governance, Risk, & Compliance
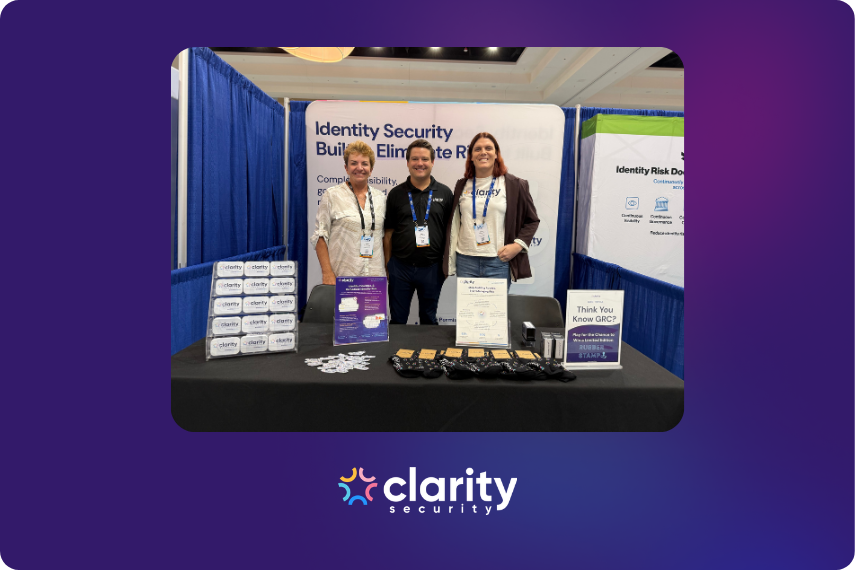
Three themes dominated ISACA GRC 2026: AI governance, the limits of compliance-first GRC, and the visibility and evidence problem. Here’s what the conversations signaled about where the field is heading.
ISACA GRC 2026: The Sessions You Shouldn’t Miss
ISACA GRC 2026 has a packed agenda. Here’s a curated session guide by role — compliance & risk, IT audit, and technology leaders — so you can plan your three days without the guesswork.
Beyond Human: What Lalit Choda and Alexis Moyse Are Telling Security Teams About Non-Human Identity and AI Agent Security

The non-human identity problem is not new. The urgency around it is. That was the through-line of a recent Clarity Security webinar bringing together Lalit Choda, founder and CEO of the Non-Human Identity Management Group and one of the industry’s most prominent voices on NHI security, and Alexis Moyse, CEO and co-founder of Clarity Security. […]
What Is Adaptive Trust and Why Your Identity Program Probably Hasn’t Reached It Yet

Adaptive Trust is the next stage of identity security maturity — moving beyond periodic access reviews to continuous assessment and automated remediation across every identity, human and non-human. Learn what it means and how to get there.
The Three Stages of Identity Security Maturity and Why Most Programs Were Built for the Wrong Problem

Our latest report, The Three Stages of Identity Security Maturity, maps the evolution of identity security through three distinct stages and makes the case that the most widely deployed model is leaving organizations materially exposed.
Growing with the Business vs. Reacting to Change: What a Scalable Identity Security Program Actually Looks Like

Learn about the three growth patterns causing security programs to fall behind, and how to create an effective strategy that scales alongside the business.
Reflections on Identiverse 2025: Identity Is the New Perimeter. So Why Are the Ports Still Wide Open?

Many orgs say “identity is the new perimeter,” but ignore the access layer. Explore why siloed visibility and forgotten governance controls are leaving ports wide open—and how Clarity helps.
Beyond the Booth: A Recap of ISACA GRC 2024

The Clarity Team recently attended the ISACA GRC Conference– here are a few key takeaways in case you missed it!
How Crowdstrike’s Incident Highlights The Dangers of Suite Solutions
The recent Crowdstrike incident made headlines around the world earlier this year, but does it highlight a bigger issue? Read this to learn more.
Strategies for Navigating Stress in Cybersecurity
Learn actionable strategies for stress in cybersecurity, from managing workloads to fostering collaboration—build a healthier, resilient workforce.