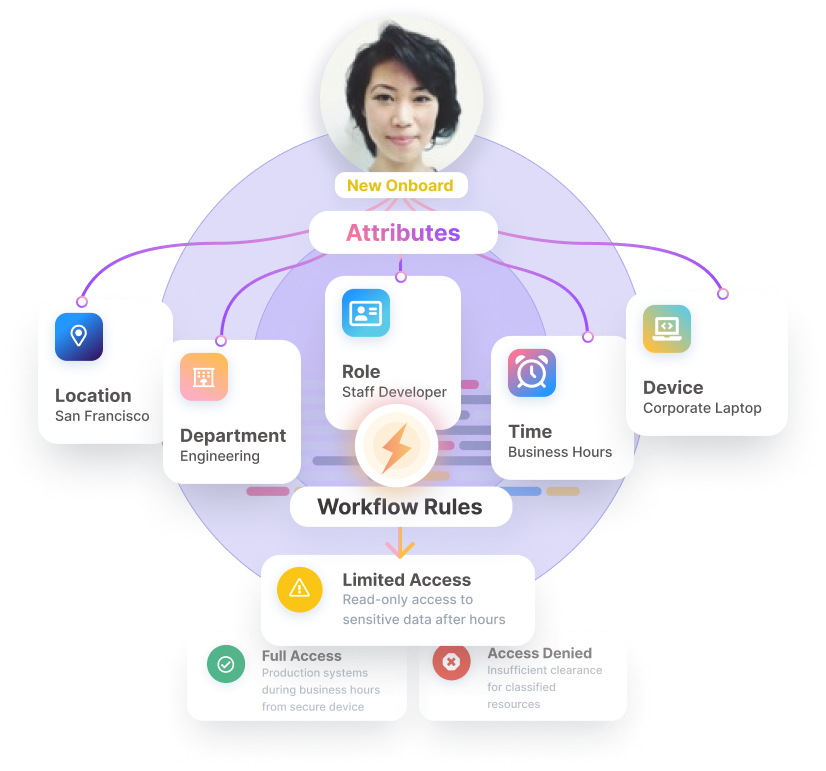
Dynamically grant least-privilege access based on real-time attributes—like job title, project, department, location, and device—so your organization stays secure, compliant, and agile without drowning in manual role maintenance.
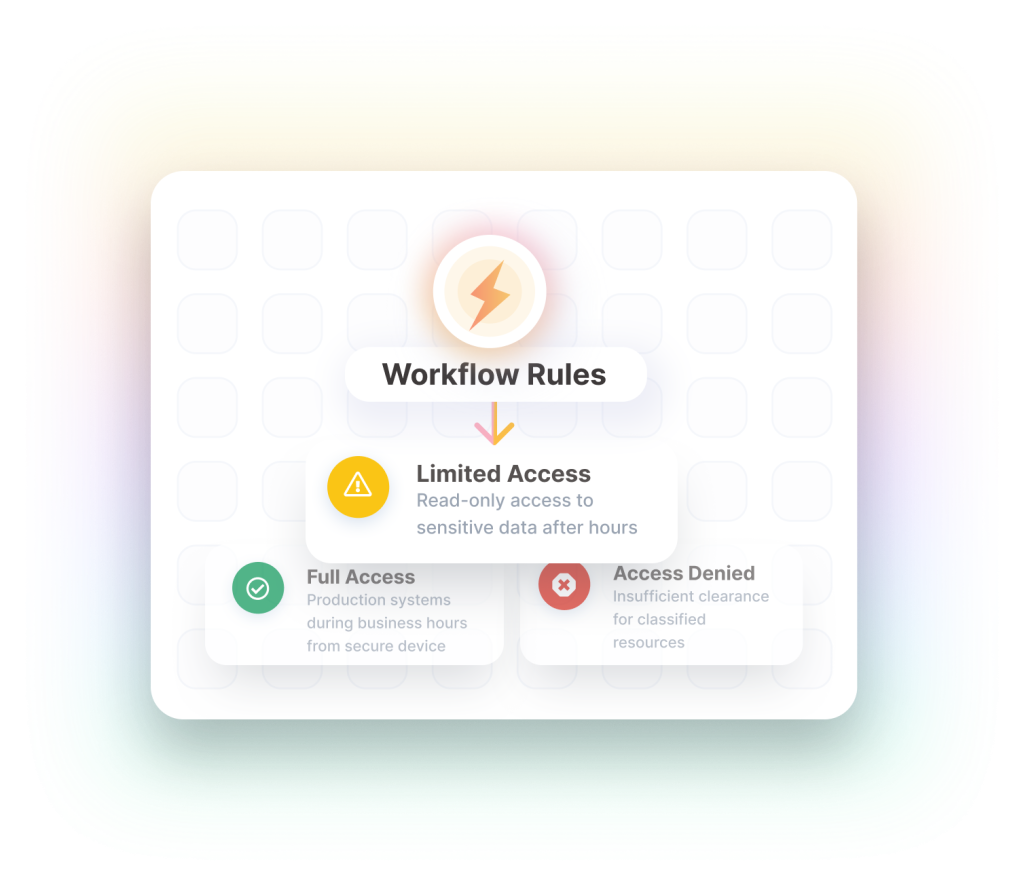
Static roles can’t keep up with high-turnover workforces or complex technology shifts. Clarity’s ABAC engine uses context-aware automation to dynamically grant or revoke permissions based on user attributes.
Whether an employee changes departments, moves to a new office, or is added to a new project, our platform handles the heavy lifting. You get precise control without the need for manual role maintenance or constant ticketing.
Eliminate Role Explosion and Manual Maintenance
Legacy role-based access control (RBAC) platforms often require teams to build and maintain thousands of individual roles.
Clarity replaces this with auto-generated ABAC profiles, complete with birthright access and policy-driven automation.
Single Source of Truth for Birthright Access
Define birthright entitlements once with attributes (like job code + location). New hires get the right access on day one — no manual provisioning, no missed accounts.
Automated Drift Detection & Remediation
Continuously monitor and remediate deviations from the “gold standard” of access and trigger alerts or remediation workflows when identities no longer match their intended profiles.
What our customers are saying...
You made it so simple. My new site is so much faster and easier to work with than my old site. I just choose the page, make the change.
Jerome Bell CTO, Waverio
You made it so simple. My new site is so much faster and easier to work with than my old site. I just choose the page, make the change.
Jerome Bell CTO, Waverio
You made it so simple. My new site is so much faster and easier to work with than my old site. I just choose the page, make the change.
ABAC is a flexible access control model that grants permissions based on the characteristics (attributes) of the user, the resource, and the environment. Unlike traditional models, it allows for fine-grained, context-aware security policies that adapt instantly as user data changes.
How does ABAC differ from Role-Based Access Control (RBAC)?
RBAC assigns permissions to static roles, which often leads to role explosion and manual maintenance. ABAC is more scalable and precise; it evaluates real-time attributes like job title, location, and department to determine access, eliminating the need to manually create and update thousands of roles.
Can Clarity Security’s ABAC work with my existing on-prem and cloud systems?
Yes. Clarity delivers unified identity governance across SaaS, hybrid, and on-prem environments. We support a wide range of protocols, including SAML, SCIM, and direct permissions for local accounts, ensuring your ABAC policies are enforced across your entire infrastructure.
Does implementing ABAC require a lot of manual configuration?
No. Clarity Security is designed to remove the manual work associated with legacy tools. Our platform automates the ingestion and normalization of identity data, allowing you to set dynamic, attribute-based rules that scale effortlessly with your business.
How does ABAC speed up the access review process?
By establishing ABAC profiles that define birthright access based on user attributes, Clarity can automatically validate standard permissions. This allows you to shift to exception-based reviews, where you only manually certify access that deviates from the automated profile. This significantly reduces the volume of items to review and simplifies the audit experience.
Three themes dominated ISACA GRC 2026: AI governance, the limits of compliance-first GRC, and the visibility and evidence problem. Here's what the conversations signaled about where the field is heading.
ISACA GRC 2026 has a packed agenda. Here's a curated session guide by role — compliance & risk, IT audit, and technology leaders — so you can plan your three days without the guesswork.
The non-human identity problem is not new. The urgency around it is. That was the through-line of a recent Clarity Security webinar bringing together Lalit Choda, founder and CEO of the Non-Human Identity Management Group and one of the industry’s most prominent voices on NHI security, and Alexis Moyse, CEO and co-founder of Clarity Security. […]